<img alt="" src="https://www.instinct365intelligent.com/810470.png" style="display:none;">

24/7 Cyber Incident Response Service & Consultancy

Strengthen resilience, reduce risk, & safeguard your organisation.

Swiftly address and recover from cyber incidents with our 24/7 support from a Celerity cyber incident response service, providing specialist support from Celerity's experienced cyber incident response consultants when you need it most.

Beyond rapid containment, our Security Consultancy helps you assess risks, optimise processes, and strengthen your overall cyber posture.  Ensure proactive readiness and long-term protection for your organisation.

Group 40043-1

Get Back to Normal Business Operations Faster

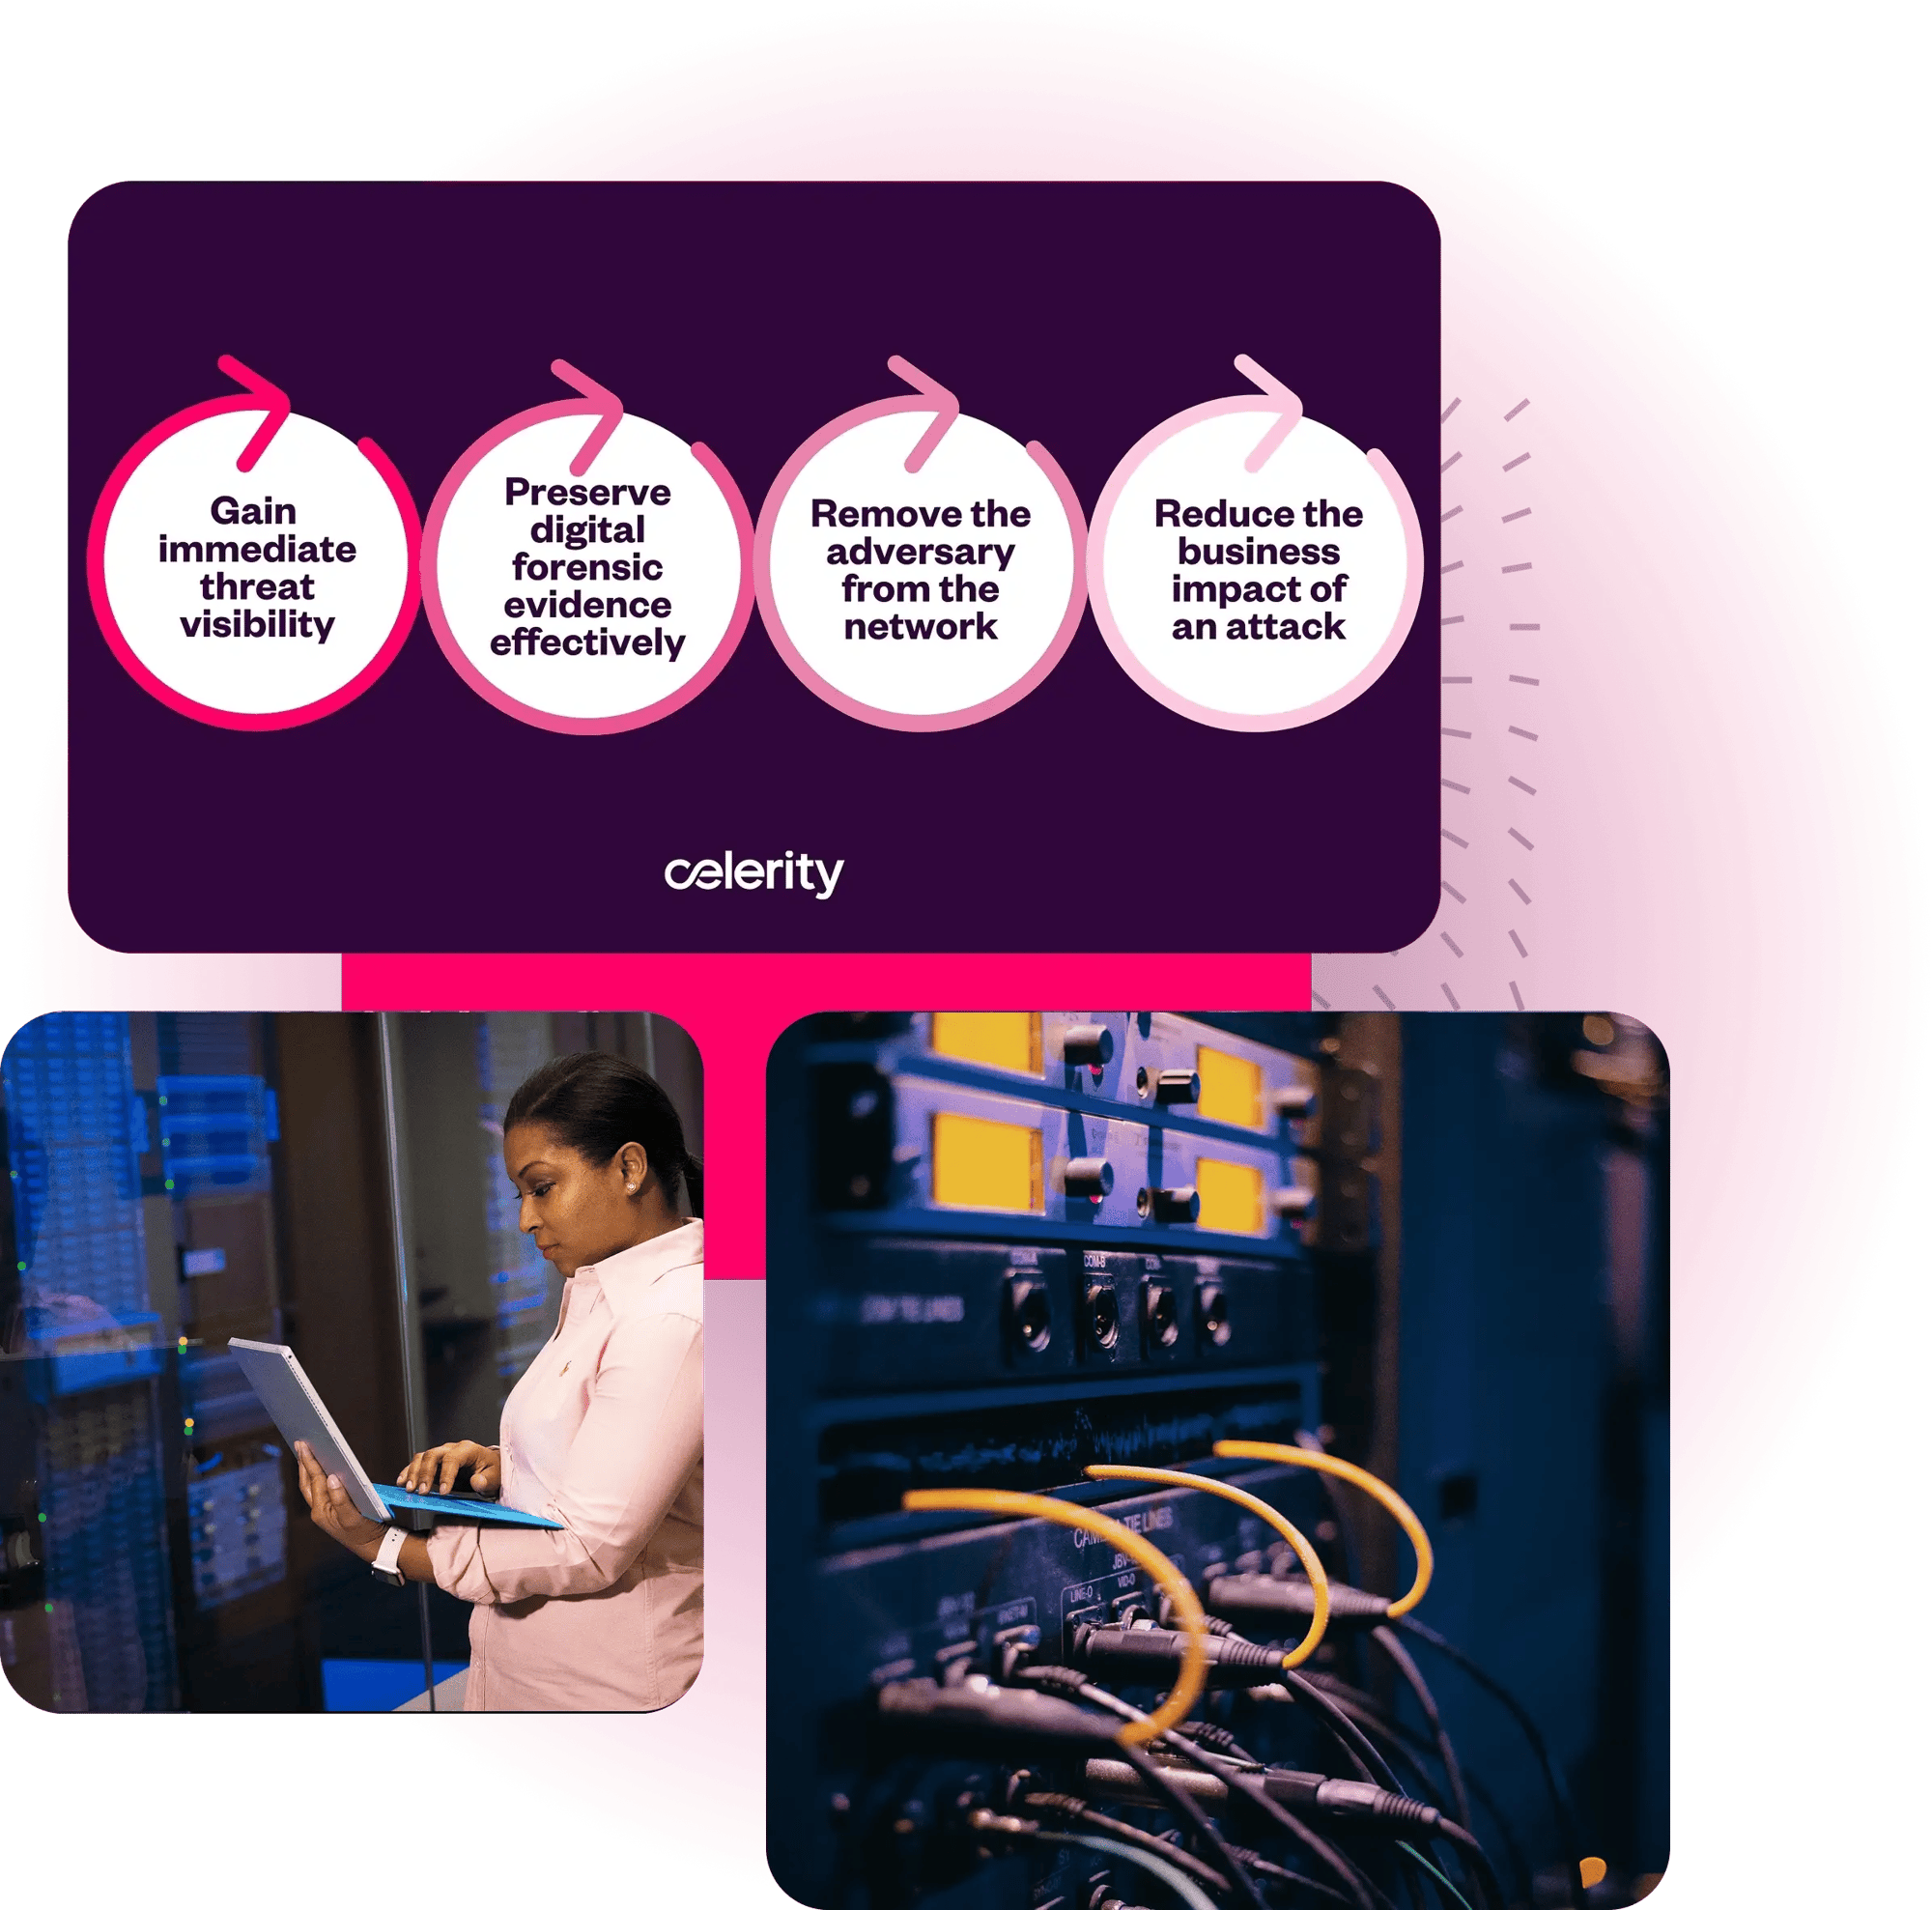
Celerity’s Incident Response service provides immediate support when a cyber incident occurs, combining AI-powered detection, real-time analysis, and rapid containment to minimise disruption and damage.

Our Security Consultancy works alongside your team to strengthen your overall security posture, providing risk assessments, compliance guidance, and strategic recommendations tailored to your organisation.

Together, these services ensure you’re not only ready to respond to incidents but also proactively reduce the risk of future threats.

Group 40076-min (1)

Your Incident Response Challenges

clipboard-list-solid 1

Lack of Preparation

Being unprepared for security incidents can leave your organisation vulnerable.

Preparation and Planning

Our tabletop exercises and incident response plans ensure your team is ready to act efficiently. Pre-agreed procedures, 24/7 hotline access, and best-practice guidelines enable a coordinated and rapid response.

circle-nodes-solid-4

Limited In-House Resource

Many organisations lack the specialised skills and budget to maintain robust security. 

Resource Augmentation

Supplement your team with our cybersecurity experts on-demand or via tailored retainer services. Reduce costs, improve efficiency, and gain access to specialist knowledge when you need it most.

file-shield-solid-Jun-23-2025-02-43-37-1102-PM

Recovery and Continuity Concerns

Inadequate recovery and continuity plans can prolong downtime and disrupt operations.

Containment and Mitigation

Pre-agreed playbooks reduce response times, while our data security and resilience services safeguard critical assets and maintain operational continuity.

Vector-Jun-23-2025-02-43-37-0261-PM

Complex Threats

Sophisticated attacks can escalate quickly if not identified and contained.

Expert Knowledge

Our Incident Response team leverages threat insights, forensic analysis, and tailored guidance to mitigate risks, reduce exposure, and strengthen your cyber posture.

shield-halved-solid-Jun-23-2025-02-43-37-1288-PM

Technology Integration & Optimisation

Disjointed security tools and processes can leave gaps in protection.

Optimised Security Operations

We streamline technology, implement best practices, and leverage AI-driven analytics to maximise the effectiveness of your security systems and improve threat detection and response.
royal-papworth
2-2
Client Success Story
Cyber Security

We understand the evolving nature of Cyber threats, but this solution helps increase our support enabling sensitive data to be more secure, and compliance has improved.

nhs-min

Our Cyber Incident Response Services & Security Consultancy

Rectangle 1084-min 2

Incident Response

When every second counts, our Incident Response team helps you contain, investigate, and recover from cyber attacks.

Be prepared with rapid response, forensics, and remediation planning to minimise damage and restore confidence.
Illustrator-Resizer-44-1024x576

Security Consultancy

Build a stronger security posture with expert guidance tailored to your environment.

Our Security Consultancy services cover assessments, strategy, architecture, compliance, and risk management, designed to align security with your business goals.


Organisations using security AI and automation extensively saved an average of $1.93 million per data breach compared with those not using these technologies.

SOURCE: 2026 IBM COST OF A DATA BREACH REPORT

When A Breach Occurs, You Need an Incident Response Team to Act Decisively.​

Layer_1-2
On-demand Team

The Incident Response (IR) team offers expert knowledge to handle complex cybersecurity incidents, minimising your exposure to threats, risks, & cost.​

icon-energetic-1-2
Technology & Tools 

A dynamic threat Intelligence platform provides real-time visibility for rapid incident response and recovery, centralising interactions to ensure a comprehensive communication audit trail.

icon-clarity-1-2
Tailored Approach 

Leverage expertise, technology, and processes to efficiently identify & contain threats. Receive critical updates & early warnings on cyber threats & malicious traffic..
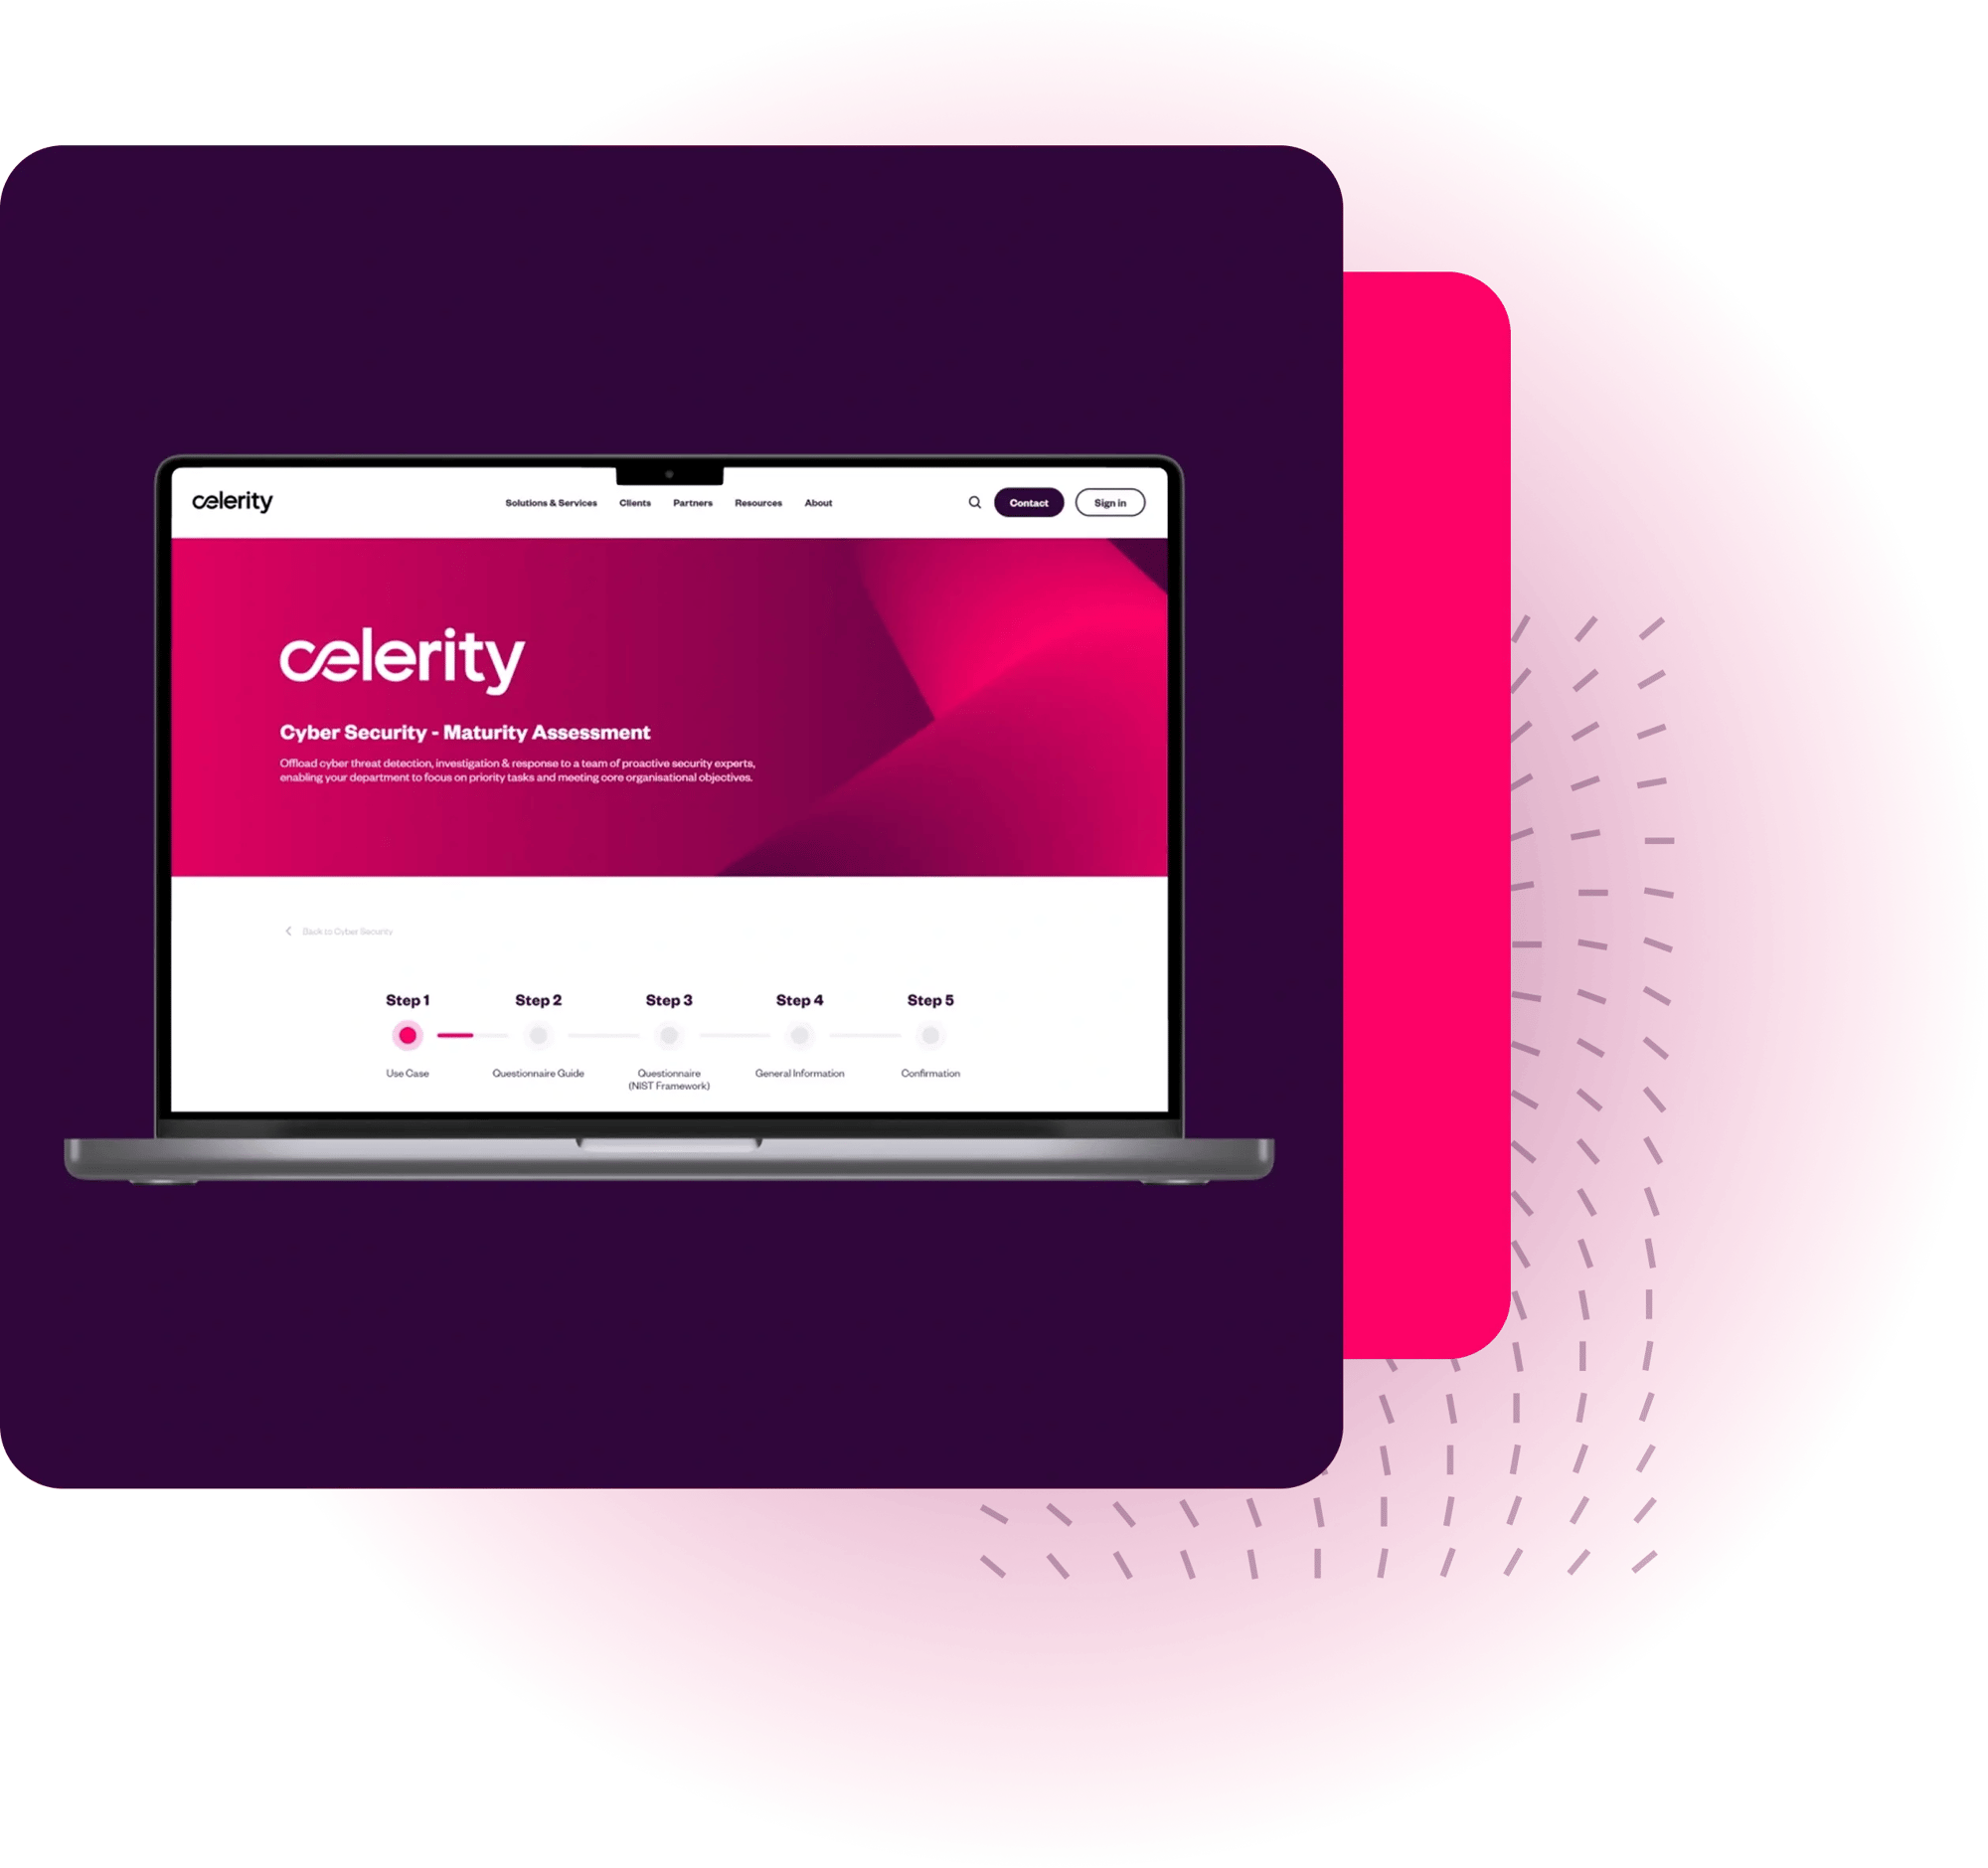
Cyber Security Maturity Assessment

Discover your organisation's cybersecurity readiness with our cyber security maturity assessment.

This structured questionnaire evaluates your cybersecurity capabilities, policies, processes, and controls, providing valuable insights into your ability to detect, respond to, and recover from cyber threats and incidents.

Gain clarity on your organisation's security posture and identify areas for improvement by completing this assessment today.

cyber-security-img-min

Respond Quickly and Strengthen Your Cyber Resilience

Reduce disruption, protect critical assets and restore business operations with support from a cyber incident response consultant.

Speak to one of Celerity's expert cyber security consultants today to discuss your incident response and security consultancy requirements. 

Businesswoman holding tablet pc entering password. Security concept-2

Cyber Security Services to Protect Against Any Threat

Managed SIEM

Managed SIEM

A scalable AI-driven cyber security platform, which tirelessly detects, analyses, and alerts on emerging threats.

Exposure Management

Exposure Management

Unify security visibility, insights, and actions across your attack surface with our AI-powered exposure management platform.

MDR & MXDR

MDR & MXDR

MDR, a comprehensive cybersecurity monitoring and rapid threat response that is tailored to your endpoints. MXDR extends beyond traditional MDR. Leveraging AI-driven analytics, machine learning, and automation. Gain enhanced visibility and control of your security posture.

Secrets & Services Management

Secrets & Services Management

Offload the complexities of secrets management to our skilled security professionals. Leverage our advanced expertise and HashiCorp Vault to centralise credentials, eliminate exposure, and strengthen your security posture across hybrid and multi-cloud environments.

Data centre worker with tablet computer in data centre

Strengthen Your Cyber Resilience with Celerity

Ready to protect your organisation against evolving cyber threats? With specialist cyber security expertise, experienced incident response consultants and a dedicated 24/7 Security Operations Centre, Celerity combines advanced technology, threat intelligence and expert-led support to help your business respond quickly and recover confidently from cyber incidents.

Our security specialists work alongside your internal IT team to investigate threats, coordinate containment, minimise disruption and strengthen your organisation's overall security posture. From developing incident response plans and conducting forensic investigations to providing strategic security consultancy, we help you prepare for potential threats while improving your ability to respond when incidents occur.

Whether you need immediate assistance with a cyberattack, on-demand access to specialist expertise or proactive support to improve your cyber resilience, our experts can help you find the right cyber incident response service for your organisation.

Frequently Asked Questions

What is a cyber incident response service?

A cyber incident response service provides specialist support to help organisations identify, contain, investigate and recover from cyber security incidents.

These services combine technical expertise, threat intelligence, forensic investigation and structured response processes to minimise the impact of cyberattacks and restore normal business operations.

What should my organisation do immediately after a cyber security incident?

If you suspect a cyber security incident, it's important to act quickly to limit potential damage.

Your first steps should include activating your incident response plan, contacting your internal security team or incident response provider, and taking appropriate steps to contain the threat while preserving evidence.

A specialist incident response team can help assess the situation, investigate the cause and coordinate recovery activities.

What types of cyber incidents can an incident response team help with?

A cyber incident response team can provide support across a wide range of security incidents, including ransomware attacks, malware infections, phishing-related compromises, unauthorised system access and data breaches.

Specialists help investigate the incident, identify affected systems, contain threats and develop remediation plans to reduce disruption and prevent similar attacks.

What is the difference between incident response and security consultancy?

Incident response focuses on identifying, containing and recovering from active cyber security incidents, helping organisations minimise damage and restore operations.

Security consultancy takes a more proactive approach, assessing existing security measures, identifying potential risks and providing strategic guidance to strengthen cyber resilience.

Together, these services help organisations prepare for incidents, respond effectively and improve long-term security.

Do I need a cyber incident response service if I already have an internal IT team?

Yes. Even organisations with established IT teams can benefit from specialist incident response support.

Cyber incidents often require advanced forensic investigation, threat intelligence and containment expertise that may fall outside the scope of everyday IT operations.

An external incident response team can work alongside your existing staff, providing additional expertise and resources when they are needed most.

How can an incident response plan reduce the impact of a cyberattack?

An incident response plan establishes clear procedures, responsibilities and communication processes to follow when a security incident occurs.

By preparing in advance, organisations can respond more efficiently, reduce confusion and coordinate containment and recovery activities.

Regular testing, tabletop exercises and expert guidance can help ensure your team is prepared to manage evolving cyber threats.

How can 24/7 incident response support benefit my organisation?

Cyberattacks can occur at any time, making access to rapid security support essential.

A 24/7 cyber incident response service provides access to specialist expertise outside normal business hours, helping organisations investigate threats, coordinate containment and minimise potential disruption.

With expert support available when incidents occur, businesses can respond with greater confidence and reduce the risk of prolonged downtime.