Cyber security teams are being asked to cover more systems, more alerts and more threats without necessarily having more capacity. For many organisations, the answer is not another security platform. It is deciding where internal expertise adds the most value, automating repetitive work and bringing in specialist support where the team cannot provide enough coverage.
That matters because the risk is already significant. The UK Government's 2025/26 Cyber Security Breaches Survey found that 43% of UK businesses experienced a cyber security breach or attack in the previous 12 months. For large businesses, that figure rose to 69%.
And the pressure isn't just about workload. The Government's latest cyber security labour market research found that 49% of UK businesses reported a basic cyber security skills gap, while 30% reported gaps in advanced technical skills such as digital forensics and penetration testing.
So how do you manage cyber security risk when your internal team is already stretched?
Most security teams have a capacity problem. Security teams may already be managing endpoint protection, firewalls, vulnerability scanners, SIEM platforms, identity controls, cloud security tools and backup systems. Each can generate information that needs to be reviewed, investigated or acted upon.
Adding another tool does not necessarily reduce that workload. The better question is: Which security activities need internal expertise, and which can be automated or handled by specialists?
That distinction matters because your internal team should spend its time where knowledge of the business makes the biggest difference.
They understand which systems are critical. They know which applications support revenue-generating processes. They understand regulatory requirements, business priorities and the consequences of taking a system offline.
Those decisions need internal ownership. Routine monitoring, alert triage and other repeatable security tasks may not.
Prioritise risk, not noise
When a team is stretched, treating every alert as equally important is a fast route to alert fatigue. A risk-based approach that tackles how to manage cyber security risk starts with the assets and services that matter most to the organisation.
The NCSC recommends taking a risk-based approach to cyber security, using resources on the things that matter most to the business rather than attempting to eliminate every possible risk. It also stresses that organisations need to understand what risks remain after security controls have been applied.
That means asking:
- Which systems are business-critical?
- Which data would cause the greatest impact if compromised?
- Which vulnerabilities are exposed to the internet?
- Which accounts have privileged access?
- Which systems would cause the greatest disruption if unavailable?
- Which risks could move quickly from a technical issue to a business incident?
For example, a critical vulnerability on an internet-facing server should generally demand more attention than a lower-risk issue on an isolated system. The objective should not be perfect security and instead be making sure limited security capacity is focused on the risks that could cause the most damage.
Automate the work your team shouldn't have to do manually
Automation can give a stretched team more capacity without requiring another permanent headcount.
Good candidates include:
- Security alert collection and correlation
- Endpoint detection and response
- Vulnerability scanning
- Patch management
- User and access reviews
- Automated policy enforcement
- Initial alert triage
- Security reporting
The NCSC recommends proportionate logging and monitoring based on an organisation's threat environment, systems and available resources. It also notes that organisations facing frequent attacks or more advanced threats may need a security operations capability able to detect and respond to those attacks.
Automation should reduce the amount of repetitive work that employees have to contend with. A useful principle is to automate the predictable, escalate the significant and investigate the unusual.
That allows security specialists to spend more time on threat investigation, architecture, risk decisions and response rather than working through an endless queue of routine alerts.
Extend your team instead of replacing it
A stretched internal team doesn't necessarily need to outsource its entire cyber security function. Often, the better model for how to manage cyber security risk is to extend what the team already does.
That might mean bringing in external support for:
- 24/7 security monitoring
- Managed detection and response (MDR)
- Extended detection and response (XDR)
- Threat hunting
- Vulnerability management
- Incident response
- Security operations
- Specialist investigations
The Government's 2025 cyber skills research found that 31% of UK businesses already outsource some elements of their cyber security, rising to 61% among medium-sized businesses. It also found that larger organisations were more likely to use outsourcing to complement their internal skills and address more complex cyber security requirements.
That is an important distinction. Outsourcing can give an internal team additional capacity and specialist expertise where it is difficult or inefficient to provide everything in-house.
What should stay internal?
Generally, internal teams should retain ownership of:
- Cyber security strategy
- Risk appetite
- Business priorities
- Security architecture
- Governance
- Regulatory decisions
- Final decisions during major incidents
What can be delivered externally?
External specialists can provide:
- Continuous monitoring
- Alert triage
- Threat detection
- Routine investigation
- Threat intelligence
- Specialist incident response
- Out-of-hours coverage
The result is a more sustainable operating model. Your internal team remains accountable for security while specialist support covers the areas where capacity or expertise is limited.
Don't forget what happens after detection
Detecting an attack is not the same as recovering from one. A security team can identify malicious activity quickly and still face significant disruption if critical systems cannot be restored. That makes cyber security and data resilience closely connected.
The NCSC recommends linking incident response with disaster recovery, business continuity and crisis management. It also specifically recommends practising response plans and restoring files from backups.
For a stretched team, this is particularly important. Ask yourself if an attacker gets through our controls today, how quickly can we recover?
That means understanding:
- RPOs
- RTOs
- Backup frequency
- Backup isolation
- Immutable copies
- Recovery dependencies
- Recovery procedures
- Who has authority to initiate recovery
A backup that has never been tested is an assumption. The NCSC's guidance for organisations choosing a managed service provider also recommends checking how backups are protected, how often they are tested and how the provider would recover services and data following ransomware.
Five questions to ask when your security team is stretched
If your team is struggling to keep up, start with these five questions.
1. What are we currently unable to monitor?
Look beyond what your security tools cover. Are there systems, cloud environments, endpoints or accounts that aren't being monitored consistently? A gap you cannot see is still a risk.
2. Which security tasks consume the most internal time?
Identify the repetitive work. If experienced security professionals are spending hours reviewing low-value alerts or producing manual reports, there may be an opportunity to automate or outsource that activity.
3. What happens outside working hours?
An attack doesn't wait for the security team to return on Monday morning. If you cannot provide 24/7 monitoring internally, decide what happens when a significant alert arrives at 2am.
4. How quickly can we contain an incident?
Detection is only useful if someone can act on it. Establish who has authority to isolate systems, disable accounts or escalate an incident. Make sure those responsibilities are documented and understood.
The NCSC recommends defining roles, escalation criteria and decision-making authority before an incident occurs.
5. Can we recover if prevention fails?
Test it. Don't assume that successful backups mean successful recovery. Your recovery process should be tested against the systems that matter most, with clear RPOs and RTOs and defined responsibilities.
Build a security model that your team can actually sustain
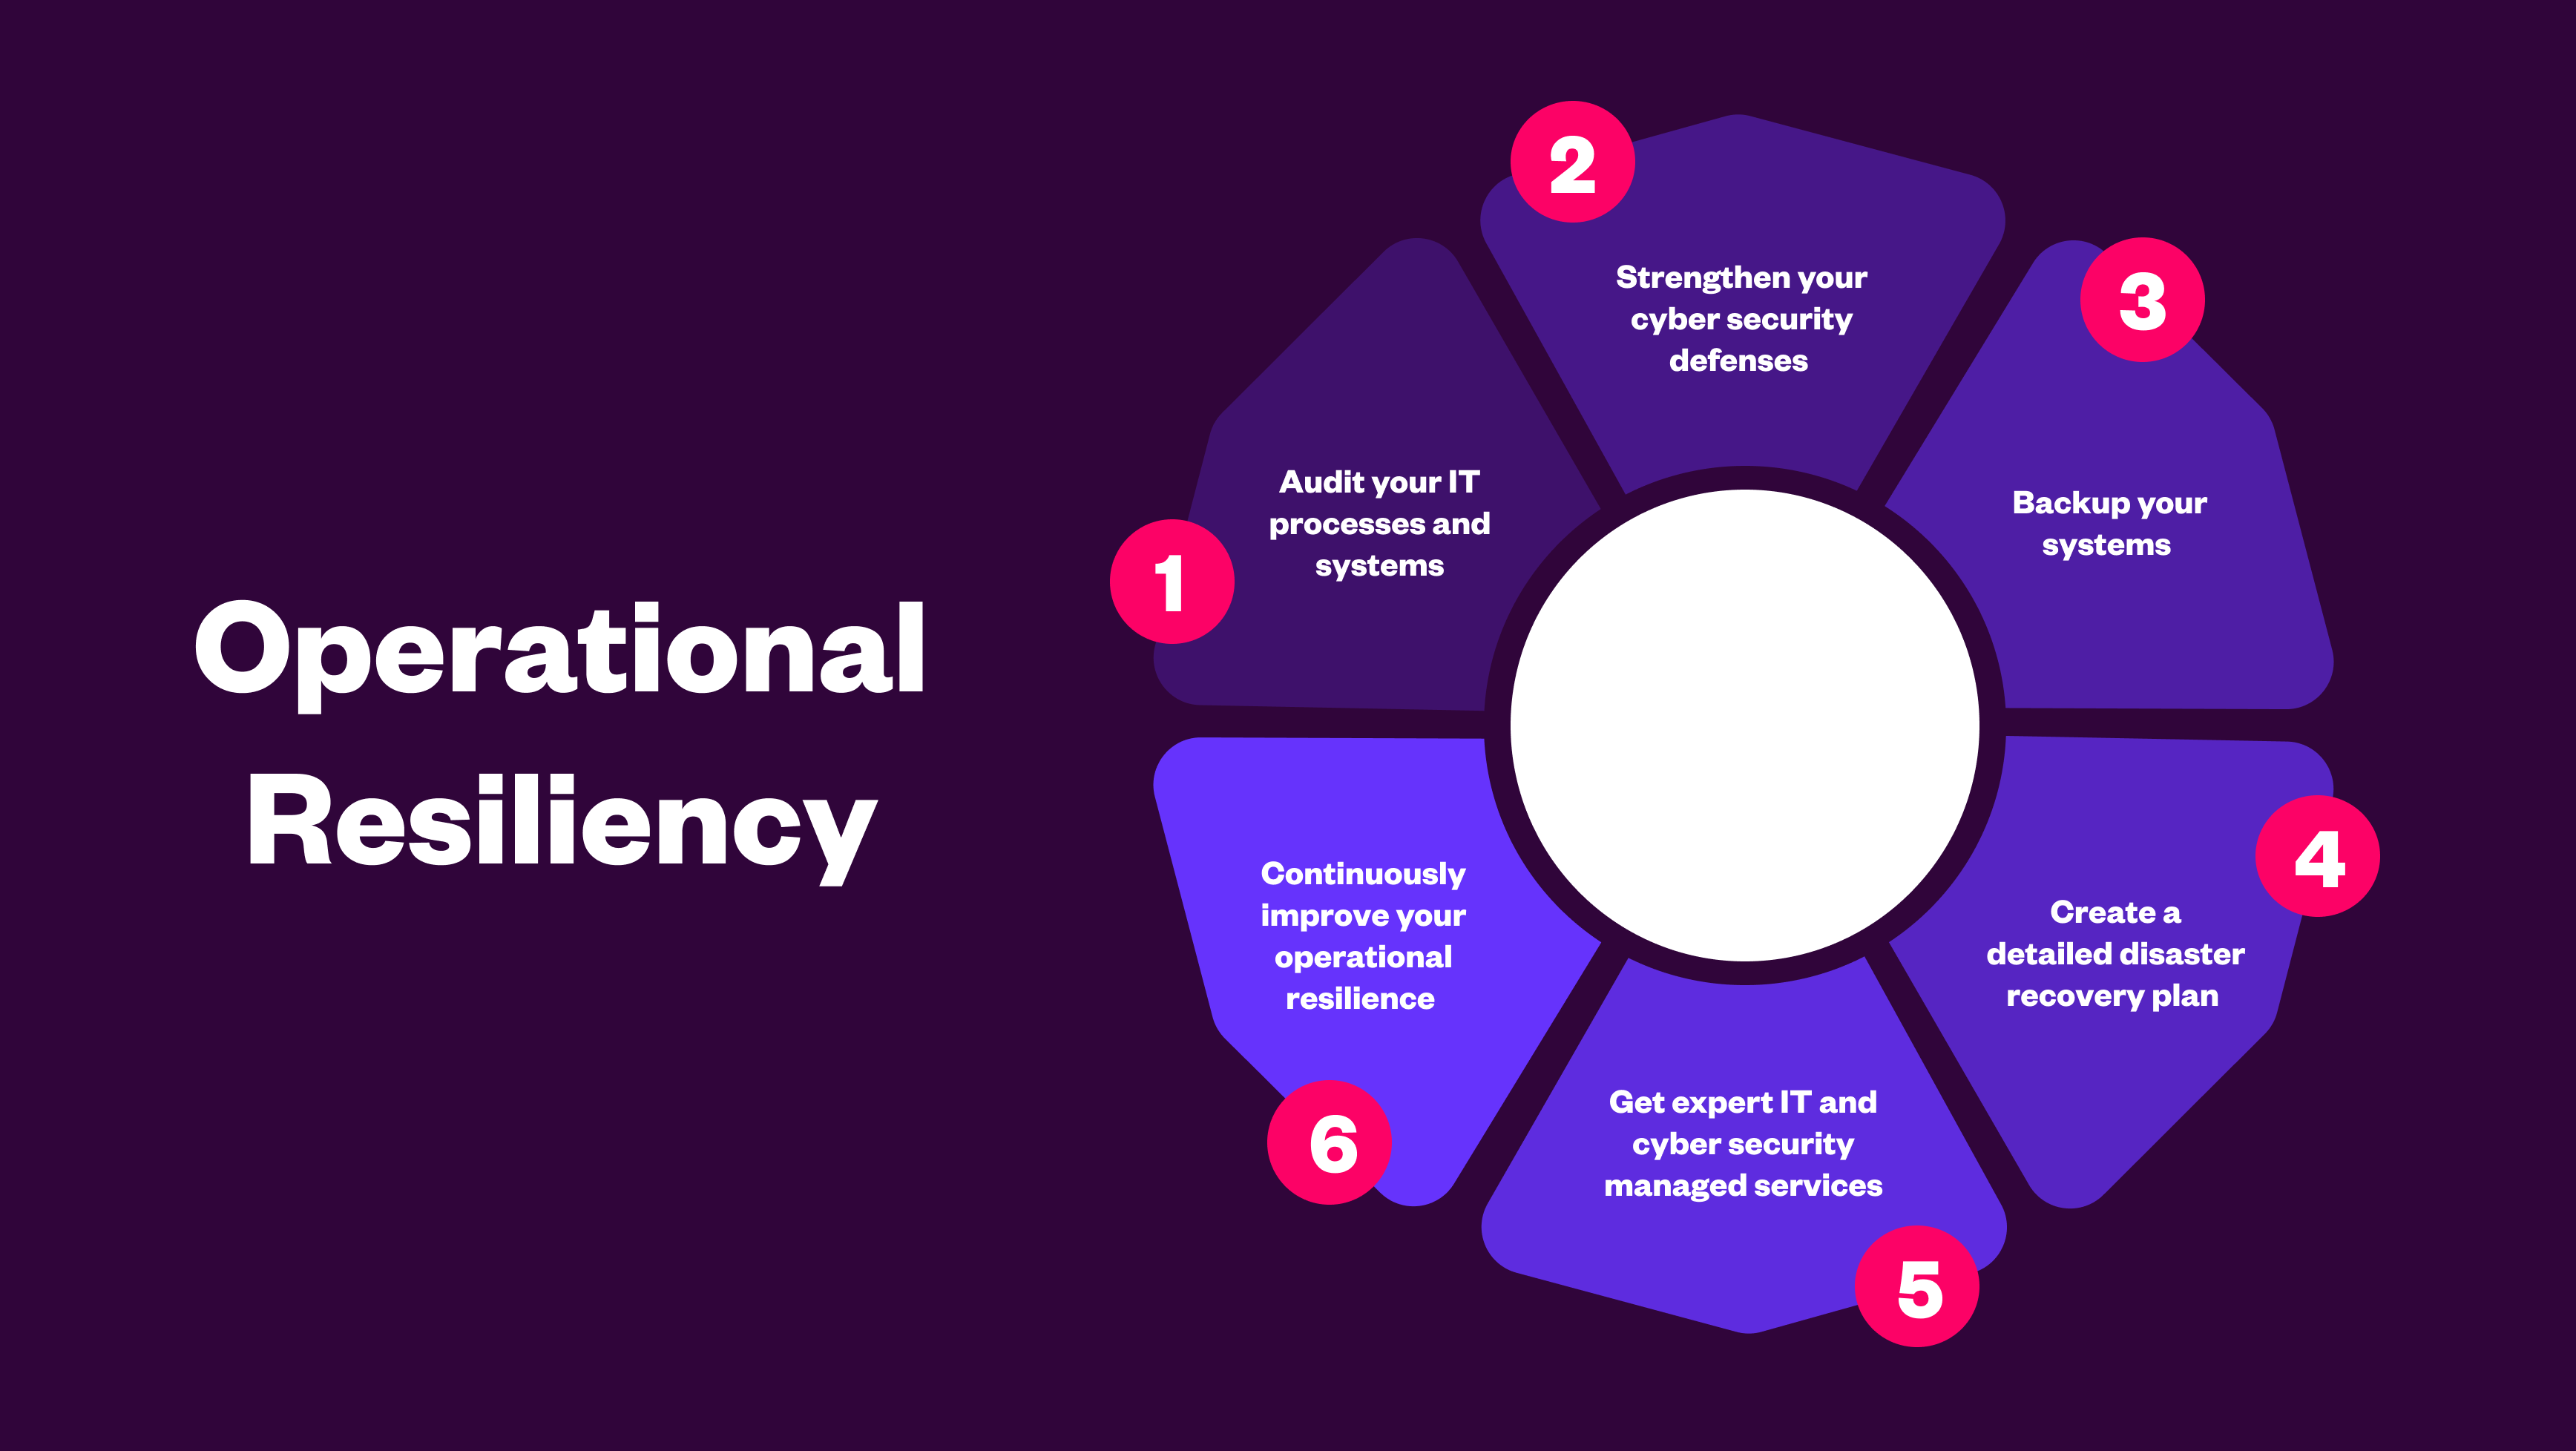
When you are considering how to manage cyber security risk, the goal isn't to make a stretched security team work harder, but focusing on how to make better use of the capacity it already has.
A practical model is:
-
Prioritise the risks that matter most to the business.
-
Automate repetitive security tasks wherever possible.
-
Extend internal capability with specialist services where coverage or expertise is limited.
-
Test detection, response and recovery before an incident exposes the gaps.
This is also where choosing an external provider requires care. The NCSC recommends checking an MSP's security arrangements, access controls, logging, incident response processes, contracts and SLAs.
It also makes clear that using a third party does not remove the organisation's responsibility for managing its security risks. The right provider should therefore add capability, not create another management problem.
How to manage cyber security risk with limited resources
Cyber security capacity is part of your risk profile. If your internal team cannot monitor everything, investigate every alert or provide specialist response around the clock, pretending otherwise does not reduce the risk.
A better approach is to understand where your team creates the most value, automate the predictable work and use specialist support to cover genuine gaps. The result is a more sustainable security operation, with internal expertise focused on decisions that require business context and external capability covering the areas where scale, specialist skills or 24/7 coverage are difficult to maintain.
Need more cyber security capacity without adding another layer of operational burden?
Speak to Celerity about managed cyber security services that extend your internal team with monitoring, detection and response expertise.