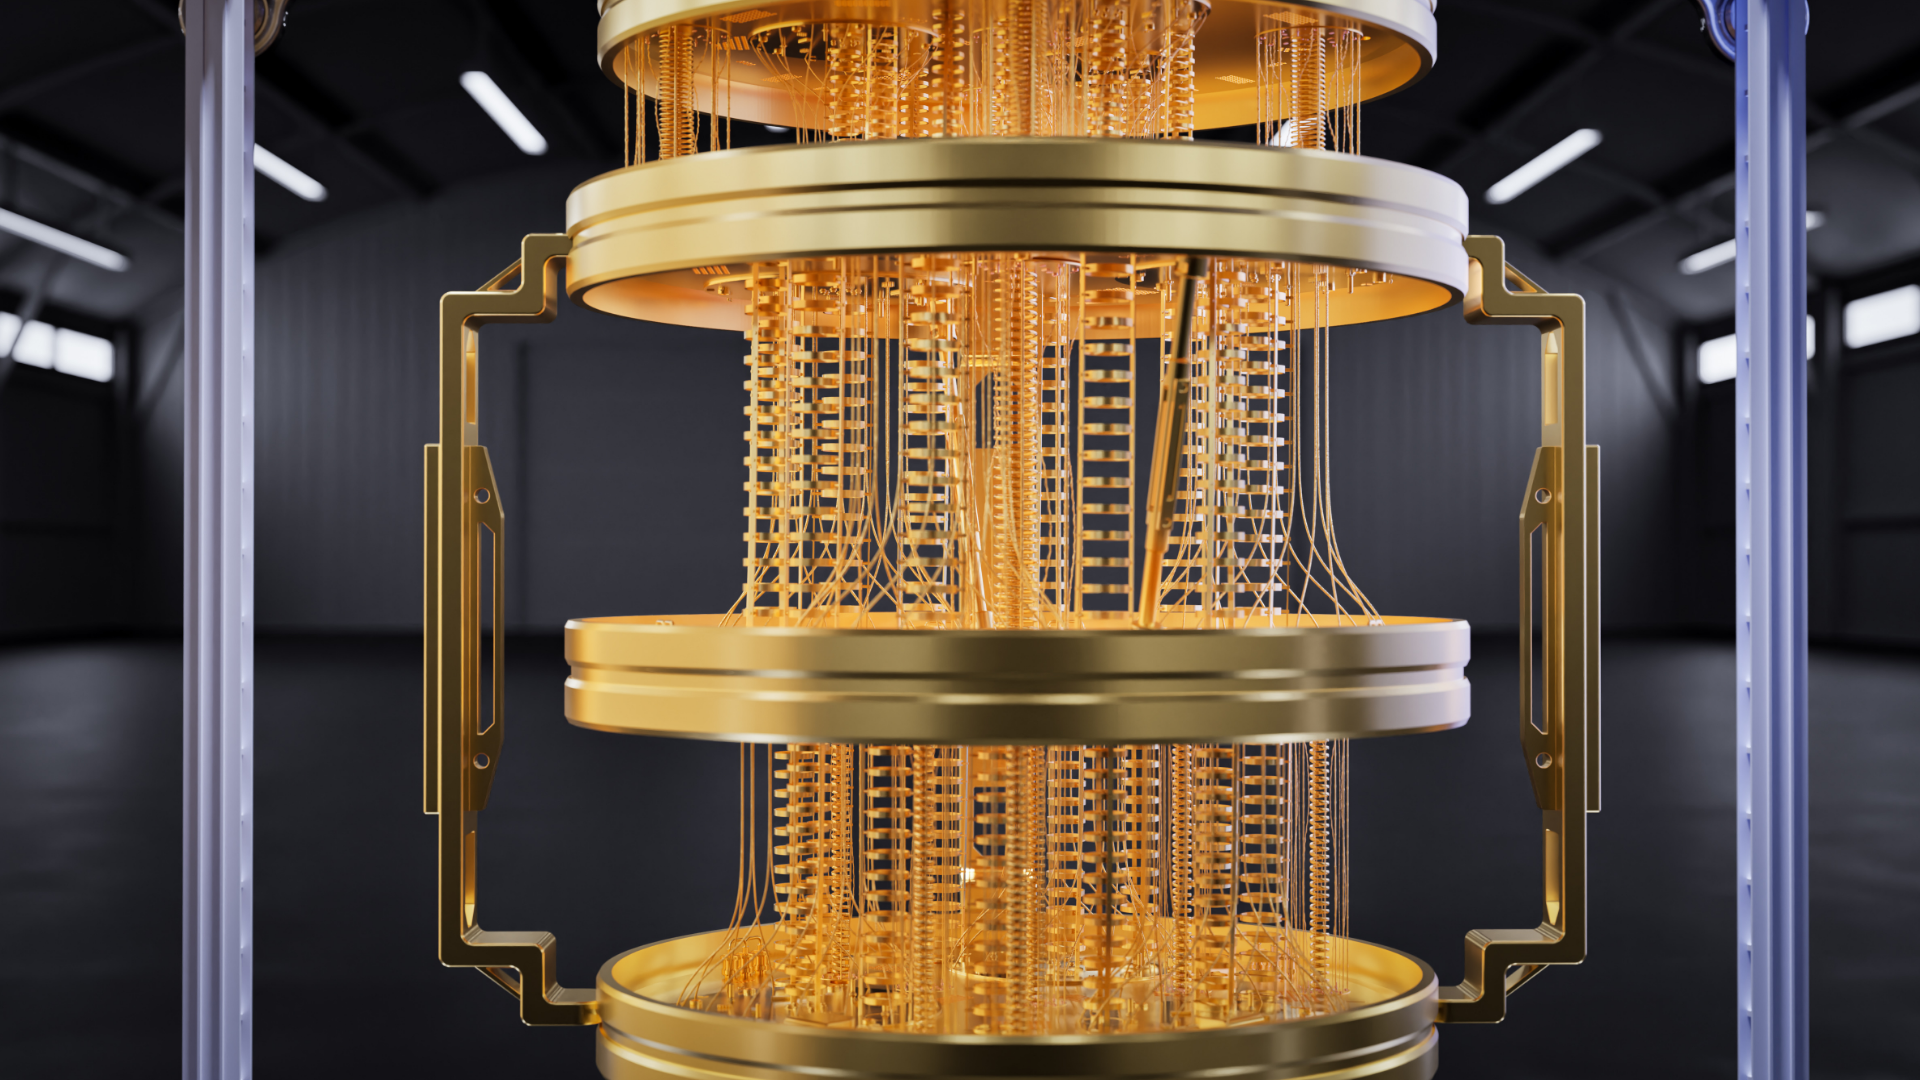
We’ve been talking to a lot of organisations lately around the subject of Quantum Computing. In particular, about the potential threat that quantum computers pose to their encrypted data.
So I thought it would be helpful to write a brief blog about what the quantum threat is, why some organisations aren’t looking to plan for remediation yet, and more importantly, what Celerity Limited and IBM can do to help you on this journey of quantum readiness to become quantum-safe.
The scary thing is that the quantum threat is already here, you just can't see it yet. Quantum computing tends to get filed alongside things that are always promising, but perpetually a decade away. That instinct has led a lot of organisations to treat post-quantum cryptography as tomorrow's problem. It isn't. The threat is happening now, and the window for action is closing faster than most security teams realise.
What is the quantum encryption threat?
Nearly every piece of sensitive data your organisation transmits or stores today is protected by public-key cryptography, algorithms like RSA, ECC, and Diffie-Hellman. These work because the maths behind them is too hard for today’s computers to crack in any reasonable timeframe. A sufficiently powerful quantum computer, running Shor's algorithm, changes that calculation entirely.
That still sounds like a future problem. It isn't, because of a tactic called "harvest now, decrypt later." Nation-state adversaries are already collecting encrypted network traffic and storing it. They can't read it today. But when capable quantum computers arrive, maybe 5/10/15 years from now, nobody knows exactly, they'll run the decryption retrospectively. Your data could be decrypted in a matter of hours. Health records, legal documents, financial transactions, intellectual property or anything sensitive when it was captured (harvested) will be exposed.
The encryption protecting that data was genuinely strong at the time. That won't matter.
This isn't theoretical. It's an active exfiltration campaign with a delayed payoff, and organisations that wait until quantum computers are publicly available to start migrating will have already lost the data.
Why are most organisations still waiting?
If the threat is real and present, why isn't it a boardroom priority? There are a few reasons, and they compound each other.
The timeline feels abstract and security teams are fighting current fires. When the breach hasn't happened yet, when the attacker is patient and the data is still technically encrypted, it struggles to compete for budget with ransomware that's making an immediate operational impact.
The problem also feels impossibly large. Most organisations genuinely don't know how much cryptography they use, where it lives, or which algorithms are running in which systems. Auditing every application, network connection, job, and certificate across a hybrid environment is incredibly daunting, so nothing starts.
Regulatory pressure has been slow to land, too. NIST only finalised its first post-quantum cryptography standards in 2024. Without a compliance requirement, many organisations treat migration as optional.
And migration is genuinely hard. Replacing cryptographic algorithms isn't like patching software. It requires understanding every place encryption is used, what data it protects, how urgent the risk is, and what the migration path looks like. Then executing it without breaking the systems that depend on those algorithms.
The result is a present-tense threat met with future-tense planning.
How Celerity & IBM can help
We at Celerity, offer a Quantum Safe Assessment, which gives your organisation the visibility it needs to understand its cryptographic exposure and begin the migration journey while there is still time to complete it. It’s a structured, IBM-led workshop delivered by Celerity experts will take your organisation from cryptographic uncertainty to a board-ready roadmap. The assessment follows a proven five-step methodology tailored to your sector, scale, and regulatory context.
IBM have a number of tools to help with the step most organisations skip, which is finding out where you actually are from a cryptography perspective.
- IBM Guardium Cryptography Manager provides visibility into your infrastructure and to wherever cryptographic objects and assets actually live. It identifies what keys, certificates and encryption is in use across the infrastructure side of your network. This allows you to prioritise migration based not just on which algorithms are weak, but on which weak algorithms are protecting the most critical data.
- IBM Quantum Safe Explorer scans your applications and source code to find cryptography that is in use and produce a Cryptography Bill of Materials, or CBOM. Quantum Safe Explorer then visualises its findings in a centralised dashboard view where you can draw actionable insights and prioritise any remediation actions that are required for quantum resilience.
- IBM Z Crypto Discovery & Inventory, for organisations running IBM Z mainframe infrastructure, addresses the "too complex to start" problem directly. It analyses cryptographic statistics from jobs, applications, and network connections across your Z environment, building a consolidated cryptographic inventory, a Cryptographic Bill of Materials, zCDI identifies which algorithms you're running, checks them against industry standards and flags anything that wouldn't survive a quantum attack. It separates classical security strength from post-quantum security categories, so you can see which workloads are exposed and how urgently they need attention.
This combination of assessment and tooling matters. Knowing you have vulnerable cryptography is one thing. Knowing it's protecting your customer payment data, or your most sensitive contracts, is what drives the right decisions.
Migration to quantum-safe takes years, which is why you can't wait
Migration to post-quantum cryptography is expected to take multiple years. The NCSC requires all organisations operating critical infrastructure or handling sensitive data to be quantum-safe by 2035. Working backwards, cryptographic migration takes five or more years, procurement two to three years, and discovery alone takes 18 to 24 months. That's not a reason to delay, it's the reason urgency matters. Every year spent not starting is a year spent exposed, with data being harvested that can't be protected after the fact.
The journey starts with visibility. You can't migrate what you can't see. Celerity’s assessment offering and IBM's tools give you the cryptographic inventory and the roadmap to reduce your exposure systematically.
Quantum computers capable of breaking today's encryption may still be years away. The window to protect your data before they arrive is open now.
Get in touch
If you’d like more information on anything Quantum related, or if you’re interested in our Quantum Safe Assessment, then please get in touch today.
Get in touch